Operations · Guide
The Impact of GDPR on CCTV Usage in Businesses
CCTV means processing personal data: signage, minimisation, retention and a lawful basis. What GDPR asks of every business running cameras.
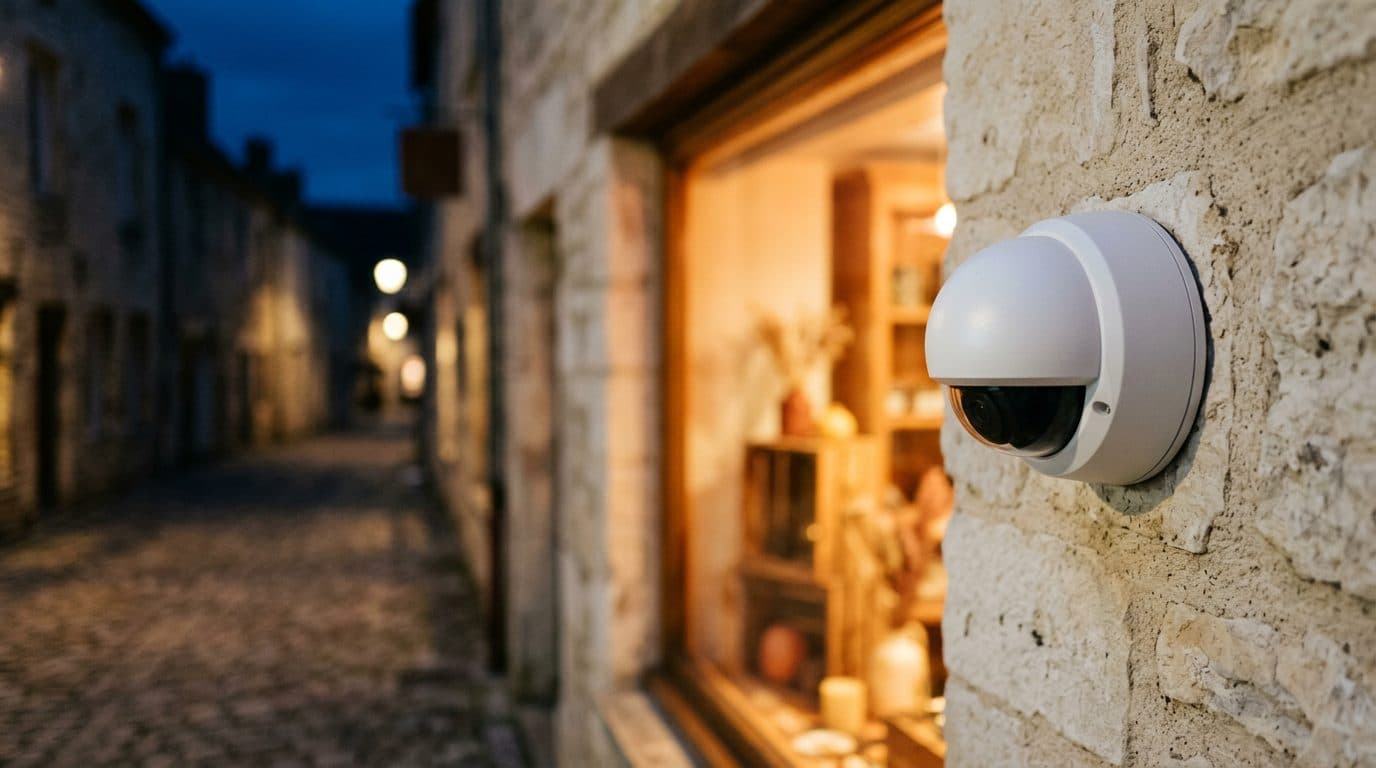
The use of CCTV in businesses has become a common practice for security and monitoring purposes. However, the General Data Protection Regulation (GDPR) imposes specific requirements on businesses using CCTV, emphasising the importance of transparency, data minimisation, and lawful processing. Recent discussions, like those highlighted by The Morning Advertiser, underscore the ongoing challenges businesses face in ensuring their CCTV systems comply with GDPR.
For businesses using CCTV, understanding GDPR requirements is crucial to avoid potential penalties and maintain compliance. One key consideration is transparency. Businesses must inform individuals that they are being recorded and provide clear information about the purpose of the CCTV, how the footage will be used, and how long it will be retained. This information should be easily accessible, such as through visible signage near CCTV cameras.
Data minimisation is another critical aspect of GDPR compliance. Businesses should ensure that their CCTV systems only capture footage that is necessary for the intended purpose. This means regularly reviewing the placement and coverage of cameras to avoid capturing excessive or irrelevant data. Additionally, businesses should implement measures to restrict access to CCTV footage, ensuring that only authorised personnel can view or process it.
Lawful processing is also essential for GDPR compliance. Businesses must have a valid legal basis for processing CCTV footage, such as legitimate interests or consent. It is important to document this legal basis and be prepared to justify it if challenged by regulators.
To ensure compliance with GDPR, businesses should conduct regular audits of their CCTV systems and related data protection practices. These audits can help identify any compliance gaps and ensure that the necessary measures are in place to address them. Appointing a Data Protection Officer (DPO) or conducting an Article 37 readiness review can provide valuable insights into a company’s data protection practices and help address any areas of concern.
At Privacy Core Services, we offer outsourced DPO appointments and Article 37 readiness reviews to support businesses in their data protection efforts. Our services can help your organisation navigate the complexities of GDPR compliance for CCTV usage and ensure that your practices align with regulatory requirements.
Sources & further reading
- News report
GDPR and CCTV: 7 key compliance rules every hospitality operator must know (opens in a new tab)
The Morning Advertiser · 7 October 2026
Is your business affected?
Running cameras and not sure your signage, retention or lawful basis would stand up? A fixed-fee review or an outsourced DPO settles it.
If this touches how your organisation handles personal data, drop us a line. We’ll talk it through with you — no obligation.