
ANÁLISIS Y NOTICIAS
Análisis
Subject Access Requests in 2026: What the Updated ICO Guidance Means
The Data (Use and Access) Act 2025 codified the reasonable and proportionate search standard. Deadlines, identity checks, exemptions, redaction and a 30-day workflow.
Artículos recientes
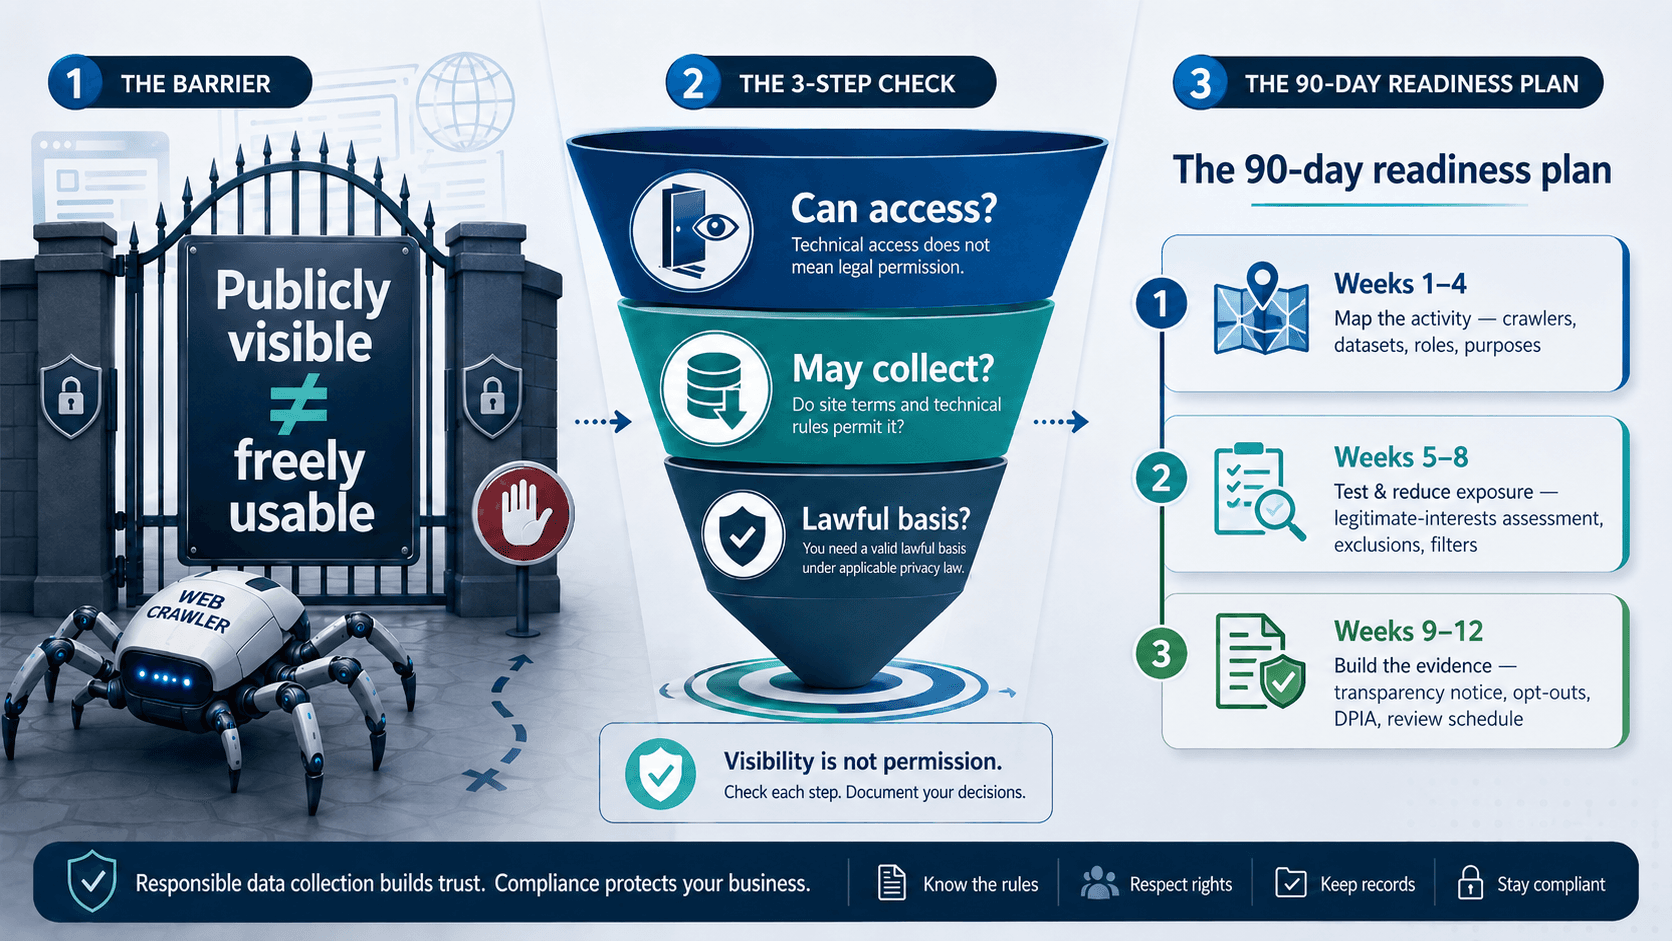
AI Web Scraping Under GDPR: What the EDPB's 2026 Guidance Means
Publicly available does not mean freely usable. What the EDPB's draft Guidelines 03/2026 require before scraping personal data to train generative AI.
Seguir leyendo →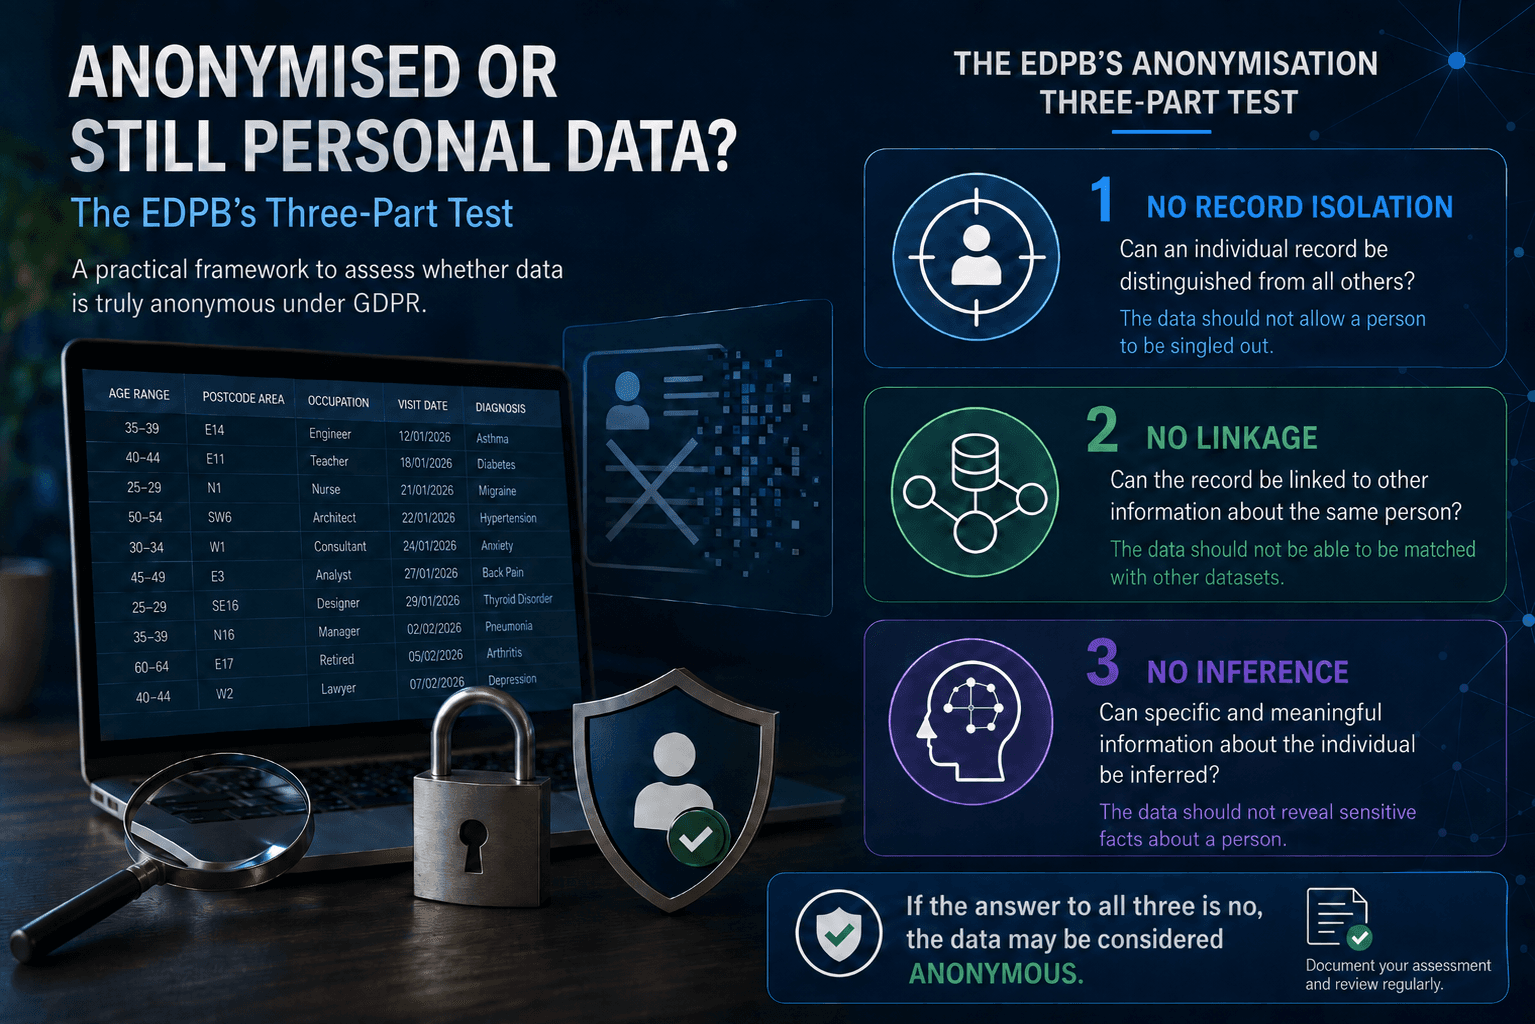
Artículos recientes
Anonymised or Still Personal Data? The EDPB's New Three-Part Test
Removing names does not make data anonymous. How to apply the three-part test in draft Guidelines 02/2026: no record isolation, no linkage, no inference.
Seguir leyendo →
Artículos recientes
EU AI Act: Where Data Controllers Stand After the 2026 Omnibus
The EU has finalised the AI Act simplification package, moving high-risk deadlines to Dec 2027. What deployers and controllers should do now.
Seguir leyendo →
Artículos recientes
Cookie Compliance: 5 Evidence Gaps Auditors Keep Finding
CMP logs, consent scope, dark patterns, and what “proof” looks like in practice across EU/UK guidance.
Seguir leyendo →
Artículos recientes
Vendor Risk in SaaS: SCCs, TIAs & Practical Controls
How to operationalise vendor reviews without slowing teams down — a tiered approach that works.
Seguir leyendo →
Artículos recientes
DPIA Done Right: Risk Triggers Your Teams Will Actually Use
Turn DPIAs into a lightweight guardrail — where they sit in tickets, PRs, and launch checklists.
Seguir leyendo →
Artículos recientes
Security Baselines Every Privacy Programme Should Adopt
From hardening and identity to logging and encryption — privacy-by-design in action.
Seguir leyendo →
Artículos recientes
Outsourced DPO: What “Good” Looks Like
Scope, independence, reporting lines and cadence — what to expect from an effective DPO engagement.
Seguir leyendo →Convierta los análisis en acción.
Si alguno de estos temas está en su hoja de ruta, lo convertimos en un plan concreto — con evidencias a prueba de auditoría desde el primer día.
«Estos análisis dieron forma a nuestra EIPD y a nuestro proceso de revisión de proveedores. Obtuvimos formulaciones y controles concretos que encajaron directamente en nuestros flujos de trabajo.»
Directora de cumplimiento, SaaS europeo